[Source: Labrador Labs]
Labrador Labs (CEOs Jinseok Kim and Heejo Lee) today announced the launch of ServerCare Plus, a solution that analyzes an operating server’s software composition, runtime status, and network exposure together.
ServerCare Plus is an upgrade of the company’s existing server security solution, ServerCare.
It goes beyond the software installed on a server. It also analyzes the programs and services that are actually running and the network ports open to the outside. When a vulnerability is found, organizations can use it to assess whether the vulnerability can actually be exploited and to decide which servers to remediate first.
The key advancement is the expansion of analysis scope from the Software Bill of Materials (SBOM) to the Operations Bill of Materials (OBOM). An SBOM records the components that make up a piece of software and their dependencies. An OBOM extends that scope to the software, operating system (OS), configurations, and network setup running in the actual operating environment.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) classifies SBOMs into six types: Design, Source, Build, Analyzed, Deployed, and Runtime. CycloneDX, the open-source SBOM standard, also supports OBOMs, which record the software composition and runtime information of operating environments.
ServerCare Plus links OS packages, libraries, running processes, services, and network ports to identify a server’s actual operational configuration. Analysis results are delivered as an OBOM in CycloneDX format.
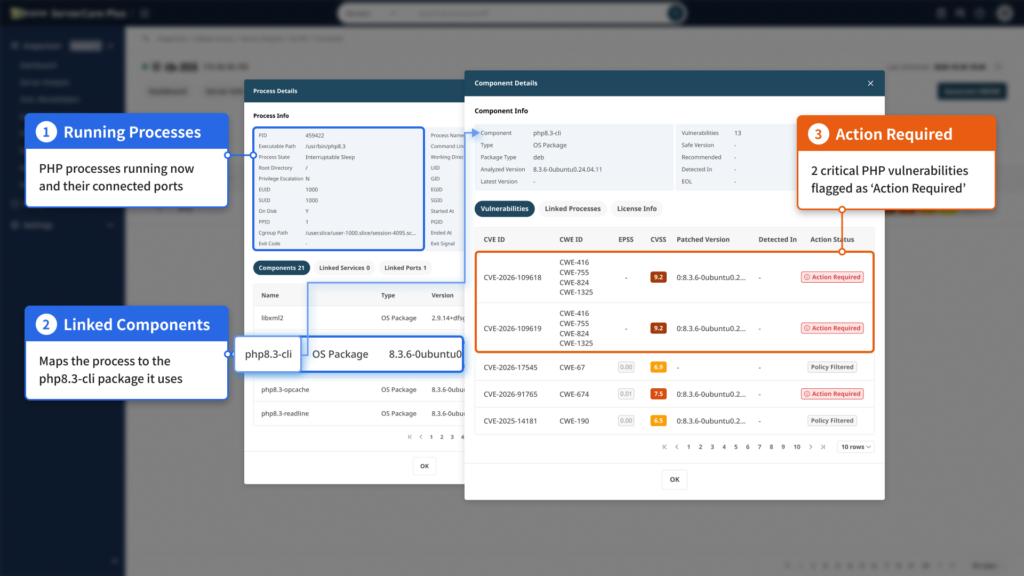
Labrador Labs cited the two recently disclosed “PHP2Shell” vulnerabilities (CVE-2026-109618 and CVE-2026-109619) as an example. PHP2Shell vulnerabilities originate in the PHP runtime environment, not in a web application’s source code or third-party libraries. The company explained that analyzing source code composition alone may not be enough to identify the operating servers that are actually affected.
Labrador Labs said it used ServerCare Plus to check the PHP packages installed on operating servers and their vulnerability information. It then analyzed how those packages relate to PHP processes that were actually running. ServerCare Plus also checked network exposure so that teams could determine which servers required action.
When a critical vulnerability emerges, organizations can check each server’s software installation and runtime status right away, without waiting for the next scheduled inspection. ServerCare Plus also uses security patch information from OS vendors to reduce false positives, where items that are already safe get flagged as vulnerable.
The solution supports security management aligned with the U.S. National Institute of Standards and Technology (NIST) server security guide SP 800-123 and its security control framework SP 800-53. It covers everything from OS security configuration checks (hardening) to remediation history management.
“If SBOM showed what software is made of, we now need to know what is actually running on our servers and where the risks are,” said Jinseok Kim, CEO of Labrador Labs. “Built on OBOM, ServerCare Plus helps organizations decide which servers to address first and respond quickly when a critical vulnerability emerges.”
[Press release source]
Byline Network, By Joonghee Kwak (https://byline.network/2026/10/29-568/)